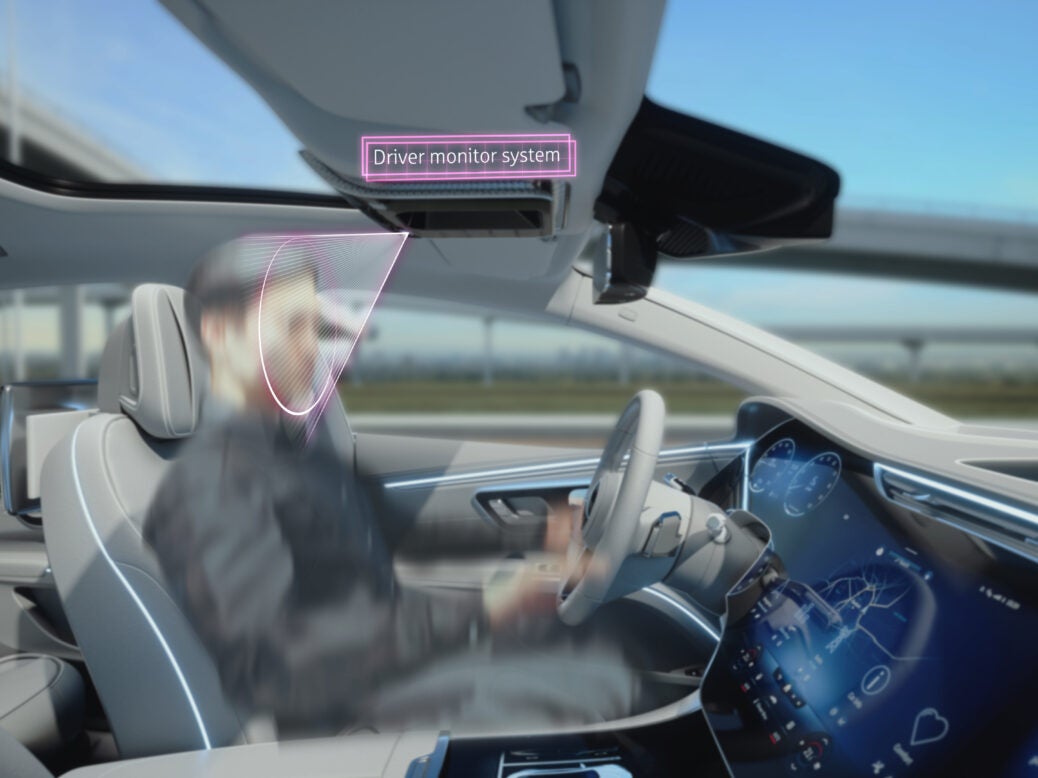
The attraction for cabin monitoring inside of a car to make sure safety and enhanced connectivity is a increasing market place, with lots of OEMs searching into this technologies for their latest types.
German semiconductor producer, Infineon Technologies, in collaboration with 3-D time-of-flight technique specialist, pmdtechnololgies, have formulated a 2nd generation of the Real3 automotive impression sensor.
This sensor will be capable to give consumers an in-depth 3D imaging company providing reliable and safe face authentication for payments, accessing private data, battery charging and extra.
We spoke to Martin Lass, promoting manager 3D ToF imager, to find out how this technological innovation functions inside automobiles as perfectly as the apps and features it will be ready to present buyers.
Just Automobile (JA): Could you clarify what time-of-flight (ToF) is and what information and facts it gives clients with?
Martin Lass (ML): The Infineon product is a 3D imager that we have produced jointly with pmdtechnololgies. The vital undertaking is now to also design a digicam about the imager since ToF is digital camera-dependent engineering. You have to have a lens on top of the imager and active infrared illumination.
You’re sending out the infrared light-weight, the gentle is mirrored, and the imager is actually comparing the transmitted sign with the gained signal. Out of that, you can estimate the length info in each and every single pixel. This is completed in an application processor and the result that you get is two sets of facts.
The first photo is the color coding, you under no circumstances get color from ToF, the shut objects would look as crimson, the much objects as blue. On top of that, you get the amplitude picture, and this is extra or much less common 2D gray- scale photo. So, you can operate typical 2D algorithms on the photograph like face ID and object detection, but on top you have the distance facts. With this information you can click on on each individual pixel and see the length information.
With this info you can then comprehend what occurring within the vehicle what are the travellers doing we can very easily distinguish involving passenger driver, what are they performing? Are they distracted? You can read through their system language.
Also, with the infrared engineering if we deliver out modulated infrared light this picture is genuinely sturdy to any gentle ailment. This is quite important to the driver if they are driving in sunny LA and there are shadows on the encounter and modifying light conditions. This is not a challenge at all to ToF.
How did the partnership with pmdtechnologies arrive to be?
We teamed up with pmdtechnologies in 2013. They wanted a very good semiconductor provider who was able to aid on the one hand higher quantity client programs and on the other side automotive.
We teamed up and have a really close cooperation in technologies improvement into products improvement, and even joint application and assistance to our buyers. At the starting and in typical, our technology enhancement is very substantially pushed by the consumer markets.
We have been the initial providers with an imager in a cell cell phone some yrs back with Google Tango, to exhibit the initial augmented fact. In today’s cell phones we have our resolution in environment experiencing but also front going through cameras for facial area ID for instance.
We launched our 1st-generation remedy at the end of 2019, now we are concentrating on our future generation imager for automotive which has a greater resolution.
What can motorists use this engineering for?
With this know-how anywhere you require to authenticate, the car or truck could do this in the history by executing face authentication in a protected way. Maybe if you want to stream your new music or obtain a video on desire whilst you are charging your EV battery or some thing for your small children, you would be in a position to do that. With our ToF imager we can do driver monitoring and also supply safe facial recognition.
The exact imager of course can be employed in a vast subject of perspective digicam to keep an eye on the entire vehicle cabin. Below we see the robust added benefits of the depth facts because you have the actual overall body model of your occupant so you can do very trustworthy measurement and excess weight estimation. You even could take out current sensors for that, so reducing some procedure costs there by including this or executing this by the digital camera and even additional significant, increase practical protection.
Perform safety is constantly a small bit challenging to promote to clients, they take this for granted, specially for today’s autos. But even in today’s automobiles you could adjust your airbag to think about how the individual is sitting down in entrance.
The know-how could also permit for effortless functionalities like gesture control which you could use if you want to change the angle of the motor vehicle mirrors, for illustration. You could modify it by seeking at it and the program would know that. Or if you get to out in the dark to the glovebox the illumination switch is automated.
Nevertheless, we are not constrained within the car, you can also do shorter range exterior answers for automatic doorways or even increase parking guide.
What is the latest standing of this technology?
This merchandise is intended and now performing in a few projects predominantly in China. I cannot say exactly where accurately, but it is utilized for facial area ID.
We have finished a demo alongside one another with our program associate Jungo Connectivity they have also employed our technologies and we had a demo in conference to demonstrate that our online video graphics array resolution can be utilised for all the driver monitoring jobs.
They also designed the 1st algorithms for 3D face authentication to present anti-spoofing because if you use conventional 2D for face ID and keep the photograph in entrance of the camera this will be detected, but with the 3D technological innovation it can quickly distinguish amongst a picture and an genuine facial area.
Secondly, we are doing work with associates on a complete occupant checking solution. This demo is concentrating on the subject matter of useful basic safety to have a incredibly correct system model wherever you can truly realize things like the spine place of the passengers to see how the spine is positioned in the seat.
You could suggest to the client if they are sitting down a very long time that it is not wholesome and they have to have a break from driving. Probably the engineering could activate a seat therapeutic massage. The options would be up to the OEM but with this our partner we can show the full demo.
What do you see the upcoming keeping for this know-how?
I consider that gesture management presents lots of benefits for instance in rear seat leisure. A lot of motor vehicles now have a nice major display screen concerning the entrance seats and if you’re sitting in the backseat you can’t reach it. Gesture management likely allows you to regulate it quickly and properly, you could convert your hand into a cursor and shift your hand to decide on some videos and push buttons.
It is the similar with basic safety functions, if you want your seat to go into chill out method how do you get to the buttons? A gesture could develop into a completely new this means in just a car or truck.
We see a potent fascination proper now from China, so I see this pattern getting driven a small little bit by China. If they are productive with it, I also see the need to have for other folks to abide by if they want to proceed marketing automobiles to China.
