New Technology Repairs and Regenerates Heart Cells After a Heart Attack

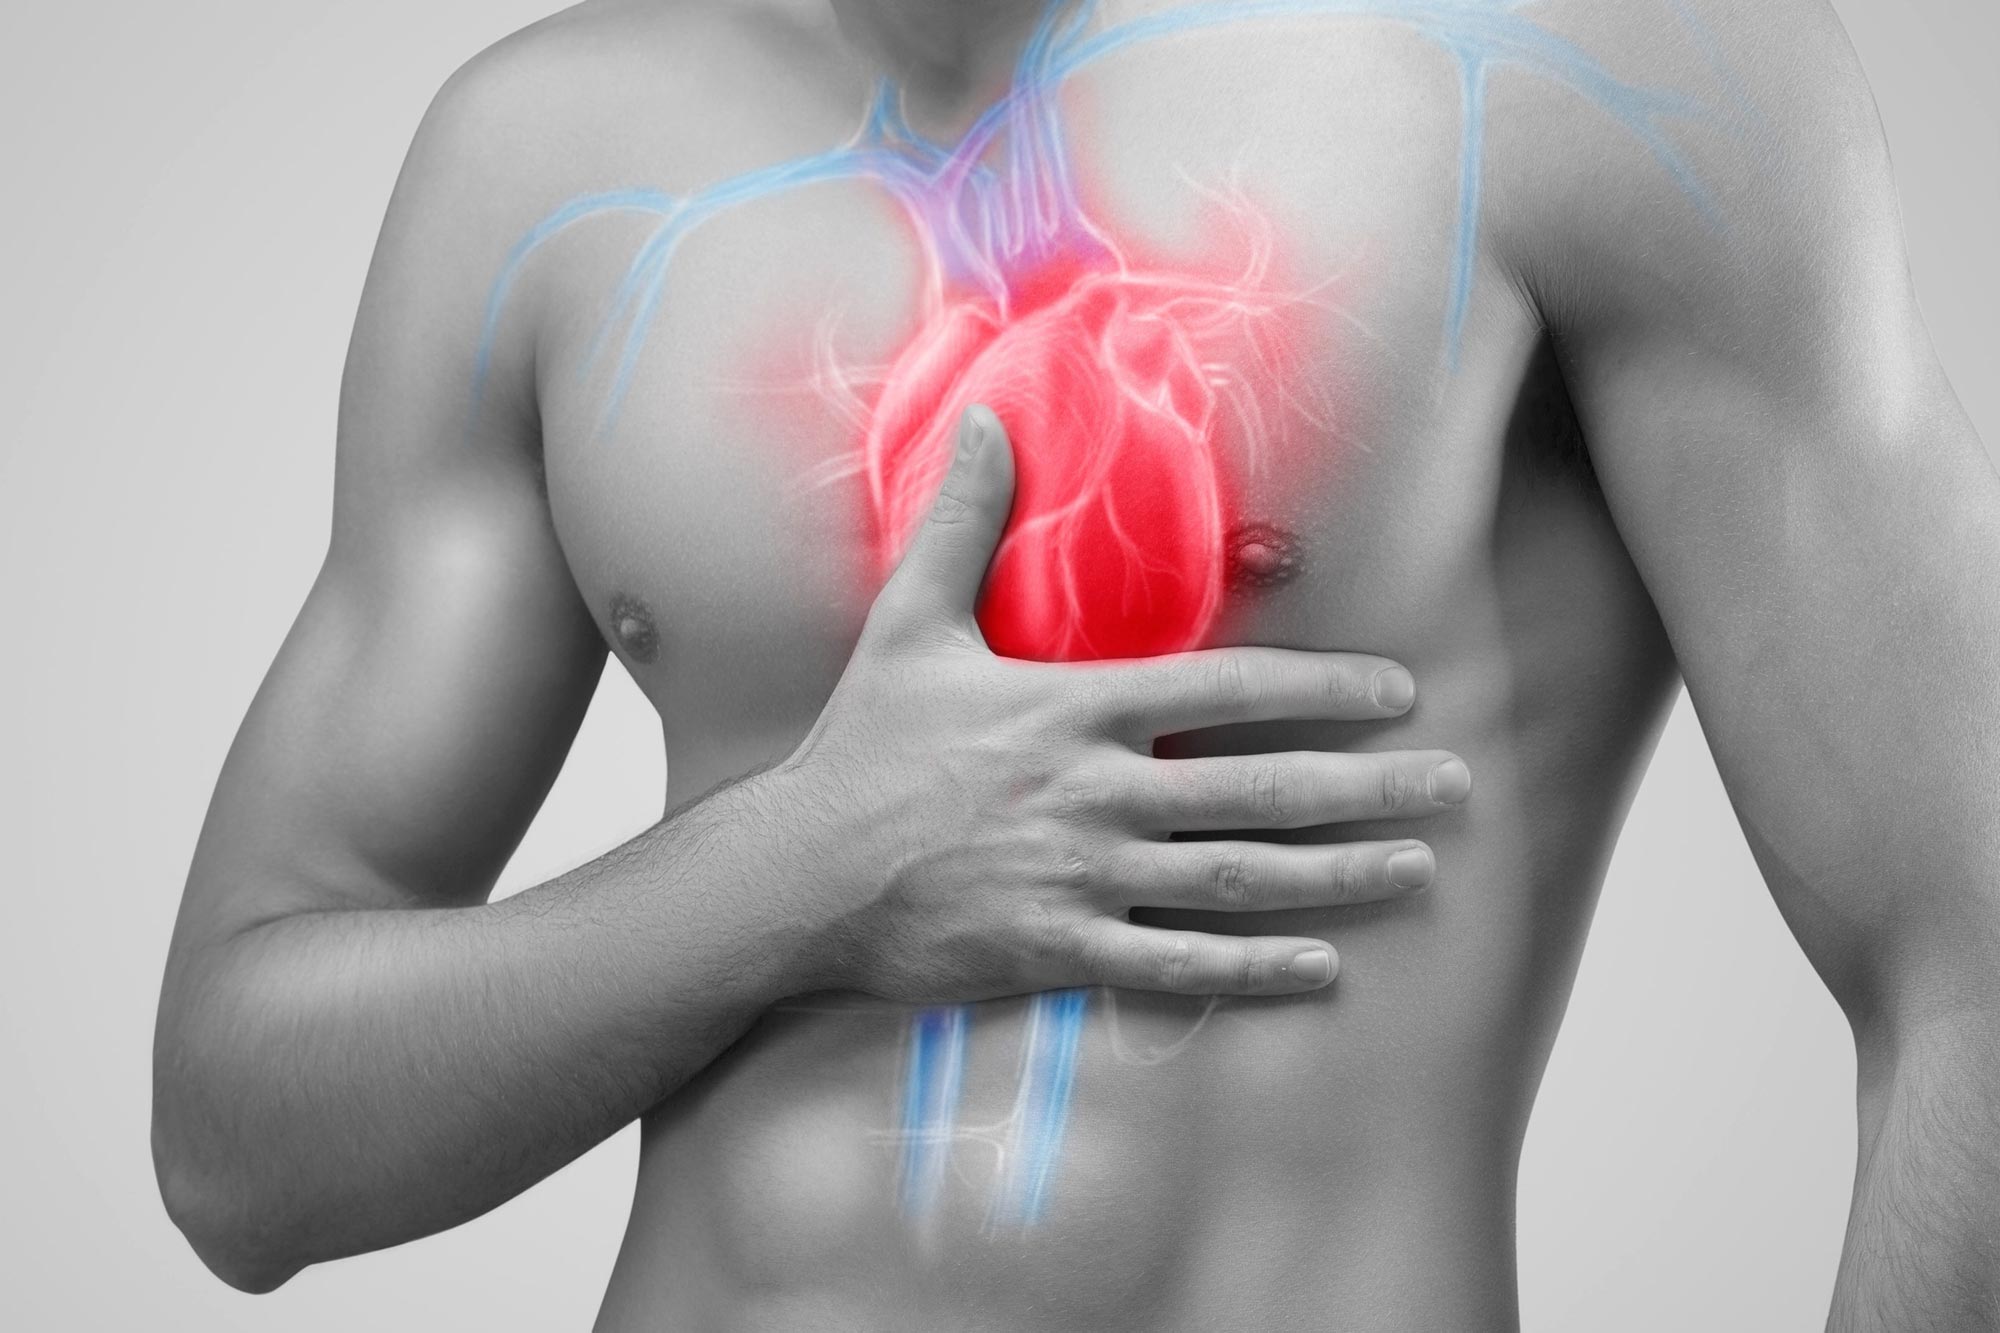
Myocarditis Young Man Heart Disease Concept

Innovative conclusions by UH scientists have the prospective to grow to be a powerful scientific system for treating heart ailment.

A “powerful scientific strategy” for managing heart ailment may final result from the latest discovery.

Robert Schwartz

Robert Schwartz, Hugh and Lillie Cranz Cullen Distinguished Professor of biology and biochemistry, led the reports printed in the Journal of Cardiovascular Growing old. Credit rating: College of Houston

College of Houston scientists have created a groundbreaking method that, in mice, not only restores the coronary heart muscle mass cells just after a myocardial infarction (or heart assault) but also can help the cells regenerate.

According to Robert Schwartz, Hugh Roy and Lillie Cranz Cullen Distinguished Professor of biology and biochemistry at the UH Faculty of Natural Sciences and Mathematics, the floor-breaking discovery, which was published in the Journal of Cardiovascular Growing older, has the possible to build into a impressive scientific technique for dealing with coronary heart illness in people today.

The progressive strategy used by the analyze workforce provides mutant transcription aspects, which are proteins that control the conversion of RNA, to mice hearts using synthetic messenger ribonucleic acid (mRNA).

“No one has been able to do this to this extent and we think it could become a possible treatment for humans,” said Schwartz, who led the study with recent Ph.D. graduate Siyu Xiao and Dinakar Iyer, a research assistant professor of biology and biochemistry.

Synthetic mRNA contributes to stem cell-like growth

The researchers demonstrated that two mutated transcription factors, Stemin and YAP5SA, work in tandem to increase the replication of cardiomyocytes, or heart muscle cells, isolated from mouse hearts. These experiments were conducted in vitro on tissue culture dishes.

“What we are trying to do is dedifferentiate the cardiomyocyte into a more stem cell-like state so that they can regenerate and proliferate,” Xiao said.

Stemin turns on stem cell-like properties from cardiomyocytes. Stemin’s crucial role in their experiments was discovered by Iyer, who said the transcription factor was a “game changer.” Meanwhile, YAP5SA works by promoting organ growth that causes the myocytes to replicate even more.

MI mmRNA Heart Treatment

The figure shows an example of a repair of an infarcted adult mouse heart in vivo, made possible through injections of a combination of STEMIN and YAP5SA mRNA. After four weeks, sectioned hearts stained red showed a significant reduction of infarcted area Credit: The Journal of Cardiovascular Aging

In a separate finding published in the same journal, the team will report that Stemin and YAP5SA repaired damaged mouse hearts in vivo. Notably, myocyte nuclei replicated at least 15-fold in 24 hours following heart injections that delivered those transcription factors.

Bradley McConnell, professor of pharmacology, and graduate student Emilio Lucero in the UH College of Pharmacy collaborated on the study by producing the infarcted adult mouse model.

“When both transcription factors were injected into infarcted adult mouse hearts, the results were stunning,” Schwartz said. “The lab found cardiac myocytes multiplied quickly within a day, while hearts over the next month were repaired to near normal cardiac pumping function with little scarring.”

An added benefit of using synthetic mRNA, according to Xiao, is that it disappears in a few days as opposed to viral delivery. Gene therapies delivered to cells by viral vectors raise several biosafety concerns because they cannot be easily stopped. mRNA-based delivery, on the other hand, turns over quickly and disappears.

A Limited Number of Cardiomyocytes

Schwartz and Iyer worked on this study for several years, and Xiao focused on this research throughout her doctoral studies at UH. She graduated in the fall of 2020.

“I feel honored and lucky to have worked on this,” Xiao said. “This is a huge study in heart regeneration especially given the smart strategy of using mRNA to deliver Stemin and YAP5SA.”

The findings are especially important because less than 1{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of adult cardiac muscle cells can regenerate. “Most people die with most of the same cardiomyocytes they had in the first month of life,” she said. When there is a heart attack and heart muscle cells die, the contracting ability of the heart can be lost.

Reference: “Mutant SRF and YAP synthetic modified mRNAs drive cardiomyocyte nuclear replication” by Siyu Xiao, Rui Liang, Azeez B. Muili, Xuanye Cao, Stephen Navran, Robert J. Schwartz and Dinakar Iyer, 19 May 2022, The Journal of Cardiovascular Aging.
DOI: 10.20517/jca.2022.17

The study was funded in part through the University of Houston, a Cullen Endowed Chair, the Texas Higher Education Coordinating Board, Leducq Foundation, and a sponsored research agreement from Animatus Biosciences, LLC.
Trust No One: New Technology Platforms Expand the Attack Surface

Next year, AT&T, Verizon and T-Mobile all plan to shut down their 3G networks, even as 5G rollouts continue around the country and around the world. And 5G isn’t just about making movie downloads and video calls faster for end consumers – it has the potential to enable entirely new classes of applications, including self-driving cars.

“The introduction of 5G into the IoT ecosystem will dramatically increase the overall surface area for attack,” said Dan Petro, lead researcher at Bishop Fox, a security testing firm.

The complexity of the overall surface area will also increase, he added.

“When no longer resource-constrained to being simple, devices will expand in complexity indefinitely,” he told Data Center Knowledge. “This is generally a recipe for security problems.”

Meanwhile, work-from-home is rapidly turning into the new normal, cloud adoption is accelerating, and APIs are proliferating.

Cyber attackers are embracing the opportunities

The expanded attack surface provides unbounded opportunities for attackers to create havoc.

Employees working from home, for example, are more vulnerable to attacks than if they were in offices, behind corporate firewalls.

And, according to a report released earlier this month by PhishLabs, phishing volume is up nearly 32{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} year-over-year, with over 8{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of corporate emails being reported as potentially malicious.

And attackers are getting more creative. Vishing attacks – using phone calls and voice messages – have more than doubled for the second consecutive quarter. Organizations are also reporting an increase of 82{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} in social media attacks since the start of the year.

Over the past 12 months, 92{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of executives said that their companies experienced a cyber attack, according to a Forrester survey released earlier this fall – and 67{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} said that these attacks targeted remote workers.

In fact, 80{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of security and business leaders said that enabling a remote workforce increased their security risks.

Meanwhile, as applications continue to become more distributed, attackers are also going after corporate APIs, usually using automation.

According to a global survey of more than 28,000 developers released last month by API platform vendor Postman, the number of APIs requests grew by 56{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} over the past year and 56{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of organizations said that they plan to increase their investment in APIs over the next 12 months, while 38{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} said they’ll keep investment level, and only 7{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} said they’ll reduce it.

Since APIs are designed to connect machines with machines, and are often exposed to the Internet, they are prime targets for automated malicious attacks.

In a report released late last month by Atomik Research and cyber security firm Kasada, 80{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of companies said that bots were becoming more sophisticated and difficult for their security tools to detect and 85{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} reported their bot mitigation solution became ineffective within a year after initial deployment.

“We’ve seen that APIs present a tempting attack surface, and there have been a number of high profile breaches and reported vulnerabilities due to insufficiently protected APIs,” said Sandy Carielli, principal analyst at Forrester Research.

According to Salt Security, API attacks increased 348{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} in the first six months of this year, and 94{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of companies had an API-related security incident in the past 12 months.

Gartner recently predicted that API attacks will become the most-frequent attack vector by 2022.

Compromised APIs played a role in the SolarWinds attack last year, and companies including Facebook, Venmo, the US Postal Service, Equifax, Instagram, Amazon, PayPal and T-Mobile have all experienced API-related breaches.

Carielli recommended that data center cyber security managers refer to the OWASP Top 10 API to understand the possible issues and work with application owners and security teams to ensure that the right controls are in place.

“It’s not simply a matter of configuring your web application firewall,” she said.

The application attack surface is also expanding dramatically.

Containers, micro-services, cloud functions – these technologies allow applications to be broken up into larger numbers of smaller pieces. As development cycles shorten, they change faster than ever before. In addition, the container model allows for the rapid scaling of applications.

“Containers often have very short lifespans – many are deployed for no more than a few minutes,” Carielli said.

Hence, traditional security management approaches no longer work. She recommended that data center cyber security managers add container security monitoring tools to look for issues like permission changes and unexpected traffic flows.

A perfect storm

This past year and a half has been a “perfect storm” for cyber security, according to the Ernst & Young Global Information Security Survey released this summer.

More than three-quarters (77{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca}) of companies said that they have seen an increase in the number of disruptive attacks over the last 12 months, up from 59{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} the year before, while 81{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} said that COVID-19 forced organizations to bypass cyber security processes.

As a result, just 9{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of boards were extremely confident that the cyber security risks and mitigation measures presented to them could protect the organization from major cyber attacks – down from 20{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} last year.

As the scale, complexity, and severity of cyber attacks keep escalating – and nation states continue to offer safe havens for attackers – security managers will need to step up their game dramatically to keep up.

The top recommendation from security experts? Shift away from a perimeter-based security approach to a zero-trust strategy.

In May, US President Biden signed an executive order instructing the federal government to adopt zero trust and to require zero trust from external cloud service providers.

In a survey released by Microsoft in July, 96{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of security decision-makers said that zero trust was critical to their organization’s success and 76{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} said that they were in the process of implementing it.

Zero trust addresses many of the issues created by the expanding attack surface. The approach can help secure devices, applications, communications, and remote users.

In an Osterman Research survey released last week, more than 90 percent of IT and security decision makers reported that their organization plans to deploy a zero trust architecture within multiple business units – or even enterprise-wide.

The respondents expect that the efficacy of their cyber security protections will double as a result.