Chinese-owned social media web page TikTok advised U.S. senators it was working on a last settlement with the Biden Administration that would “fully safeguard consumer facts and U.S. nationwide safety pursuits,” according to a TikTok letter viewed Friday by Reuters.
The letter dated Thursday arrived in reaction to inquiries elevated in a June 27 letter by a several senators including Republicans Marsha Blackburn and Ted Cruz, TikTok stated.
TikTok, owned by Chinese technologies conglomerate ByteDance, is 1 of the world’s most popular social media apps, with far more than 1 billion active consumers globally. It counts the United States as its largest marketplace.
TikTok Chief Executive Shou Zi Chew instructed senators in the letter the small video app was performing with Oracle Corp on “new highly developed information protection controls that we hope to finalize in the around long term.”
Final thirty day period, TikTok claimed it experienced finished migrating U.S. users’ details to servers at Oracle but it was however applying U.S. and Singapore data centers for backup.
TikTok’s letter acknowledged that China-centered staff “can have access to TikTok U.S. user info subject matter to a collection of robust cybersecurity controls and authorization approval protocols overseen by our U.S.-based stability group.”
TikTok mentioned it predicted “to delete U.S. users’ guarded info from our personal systems and completely pivot to Oracle cloud servers positioned in the U.S.”
TikTok has sent a response to the senators’ letter, a firm spokesperson stated in a assertion to Reuters. “We appear forward to connecting with users of Congress to talk about the material of our letter.”
TikTok is functioning to make U.S.-based engineering capacity to even further minimize the have to have for facts access throughout regions, the spokesperson added. Senator Blackburn, of Tennessee, reported TikTok “should have occur cleanse from the start off but as an alternative experimented with to shroud their do the job in secrecy.” She claimed TikTok requires to “come again and testify prior to Congress.”
The TikTok letter came just about two several years soon after a U.S. national protection panel ordered ByteDance to divest TikTok for the reason that of fears that U.S. person details could be handed on to China’s communist government.
That order was not enforced following Joe Biden succeeded Donald Trump as U.S. president last calendar year. The panel, nevertheless, known as the Committee on International Investment in the United States (CFIUS), is however conducting a national safety evaluation of the organization, according to the letter.
“We know we are amongst the most scrutinized platforms from a safety standpoint and we aim to remove any doubt about the security of U.S. person details,” the letter claimed.
TikTok has stated in the past that workers in China have facts accessibility to U.S. consumer data. In a 2020 blogpost Roland Cloutier, TikTok’s chief information and facts stability officer, reported, “Our objective is to limit knowledge obtain across regions so that, for instance, workforce in the APAC area, including China, would have incredibly nominal entry to person info from the EU and US.”
A BuzzFeed story in June showed ByteDance engineers in China experienced accessibility to U.S. details between September 2021 and January 2022.
Shared algorithms
The letter also explained “ByteDance formulated the algorithms for both equally Douyin and TikTok, and as a result some of the exact same underlying standard technologies making blocks are used by each products.” TikTok is recognized as Douyin in China.
But TikTok’s small business logic, algorithm, integration and deployment of units is specific to the TikTok software and separate from Douyin, the letter said.
Reuters beforehand described that when the code for the application, which establishes the look and sense of TikTok, has been divided from Douyin, the server code was however partially shared throughout other ByteDance merchandise. The server code presents simple performance of the apps this sort of as info storage, algorithms for moderating and recommending information and the administration of person profiles.
The Chinese government took a stake and a board seat in a crucial ByteDance entity in 2021.
TikTok spelled out in its letter to the senators that its acquisition of 1{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} of Beijing Douyin Data Service Ltd was essential to get a news license in China.
WASHINGTON–(Enterprise WIRE)–The Atlantic Council and the Krach Institute for Tech Diplomacy at Purdue jointly hosted an special briefing showcasing U.S. Underneath Secretary of Commerce for Business and Protection Alan Estevez and World wide Tech Stability Fee co-chair and former Under Secretary of Point out Keith Krach. Less than Secretaries Estevez and Krach reviewed the World-wide Tech Safety Commission’s urgent mission of securing substantial tech from the rising techno-authoritarian threats. The Fee also has the support of lawmakers and private-sector leaders at a time when the United States is working to unite its Transatlantic and Indo-Pacific allies and partners throughout a variety of crucial technological know-how issues.
“It’s a good honor to be here with Alan as we launch the Worldwide Engineering Stability Commission. It just appears like a few months ago I was here with President Biden’s ‘Asia Czar’ Kurt Campbell. We have been conversing about developing alliances with the ‘Rely on Theory.’ We appreciated his guidance for the Krach Institute and this Fee as very well,” claimed Keith Krach. The previous CEO of DocuSign and Ariba ongoing: “China’s endeavor to portray itself as a misunderstood and perfectly-intentioned world-wide lover has failed. Organizations carrying out organization with China have endured parasitic joint ventures, blatant thievery of intellectual property, a earth-huge bullying spree, and the coerced collection of proprietary technology. Company boards significantly understand performing small business with, in, or for China represents large hazard and why a lot of highly regarded board associates are demanding a China contingency plan from their CEOs.”
“Any American firm, and undoubtedly any allied organization as very well, requires to be looking and assessing their chance calculus based mostly on what’s going on in the earth right now. …I’ve specified a ton of imagined to the need to safeguard our engineering from our adversaries who will use it towards other nations and frankly, towards us, as very well as their personal folks. I see my position at Commerce as the job to deny our adversaries entry to people superior systems,” mentioned Under Secretary Estevez at his initially general public appearance in his recent purpose. He concluded, “I am extra than pleased to get the job done with the Krach Institute and am all in on the Commission.”
The Commission’s World Tech Protection System is built to complement the latest multinational endeavours to counter authoritarianism, such as the Indo-Pacific Financial Framework and Foreseeable future of the World wide web Declaration, by creating a public-non-public coalition to advertise democratic have faith in principles, electronic have confidence in criteria and common adoption of trustworthy technologies emphasizing transparency, reciprocity and adherence to global regulation.
A few components make the Commission’s scope uniquely strategic for countering techno-authoritarian threats. To start with, the Commissionwilltarget on in-depth strategies in 17 significant tech sectors and integrate them into an overarching Worldwide Tech Protection Strategy. Second, the scope will be international and private sector led, with commissioners from international businesses and establishments symbolizing additional than a dozen nations around the world as part of democracies’ common energy to contend in emerging systems. Third, even though prior commissions have principally focused on evaluation of challenges with tips confined to defensive guidelines, the World-wide Tech Stability Fee will integrate offensive and defensive methods whilst starting to develop the World-wide Tech Have faith in Community, define overarching Tech Have confidence in Standards, and accelerate the adoption of reliable engineering.
Krach also sent a briefing on leveraging Tech Diplomacy to build trustworthy alliances with the Biden Administration’s Coordinator for Indo-Pacific Affairs at the U.S. National Protection Council, Kurt Campbell, exactly where Campbell pointed to the continuation of guidelines initiated by Krach’s staff through his public services: “One of the rarest factors in government is continuity of applications because when a new govt will come in, they think, ‘I’ve received a much better plan and I am heading to do it in different ways.’ Pretty much all the operate that Keith did at the State Office, together with trustworthy networks, the Blue Dot initiative, and many others., have been followed on in [the Biden] Administration and, in several respects, which is the maximum tribute.”
The briefing culminated with highly effective remarks from former President of Estonia and World wide Tech Protection Commission Co-Chair Kersti Kaljulaid, who emphasized that all the technologies that China and Russia have is controlled by their governments. She mentioned, “They overreach using their economic could to check out to conquer the globe. They can subdue their individual citizens, their have folks, extra proficiently and efficiently, of course, applying engineering. The Cost-free World is now going through the take a look at. We require to adhere jointly. It may get time, but we will prevail. But of course, we do not prevail all by ourselves. We will prevail due to the fact we cooperate. And for that we require World wide Tech Security Commission. So, thank you, Krach Institute for Tech Diplomacy and Atlantic Council for this possibility.”
The Krach-Estevez event continues the Krach Institute for Tech Diplomacy at Purdue’s bipartisan tactic to Tech Diplomacy. In addition to ongoing engagement with both sides of the aisle on Capitol Hill, as properly as with the Condition and Commerce Departments, the Institute’s Chairman Keith Krach and Director Bonnie Glick have been invited by U.S. Secretary of Commerce Gina M. Raimondo to present tips on the nationwide critical of securing the semiconductor source chain.
About the Krach Institute for Tech Diplomacy at Purdue:
The nonpartisan Krach Institute for Tech Diplomacy at Purdue is the world’s preeminent institution targeted on Tech Statecraft, a new design of diplomacy that bridges the higher-tech sector with the overseas plan and national security sectors to guarantee reliable technological innovation is used to advance flexibility. The Krach Institute for Tech Diplomacy is a 501(c)(3) that leverages Purdue’s power in innovation, deep abilities in technology, and world-wide prowess in educating transformational leaders. It focuses on rallying our allies, leveraging the innovation of the private sector, and amplifying democratic values centered on rely on.
For extra information and facts, go to techdiplomacy.org. Abide by the Krach Institute for Tech Diplomacy at Purdue on Twitter, LinkedIn, and YouTube. You should get hold of push@atlanticcouncil.org and techdiplomacy@prf.org for media inquiries about the World wide Tech Protection Fee.
Nina Jankowicz’s new guide, “How to Be a Lady On-line,” chronicles the vitriol she and other ladies have confronted from trolls and other malign actors. She’s now at the center of a new firestorm of criticism, this time over her appointment to direct an advisory board at the Department of Homeland Stability on the menace of disinformation.
The generation of a board, declared final 7 days, has turned into a partisan fight more than disinformation itself — and what job, if any, the authorities really should have in policing phony, at periods poisonous, and even violent material on-line.
Within hrs of the announcement, Republican lawmakers began railing from the board as Orwellian, accusing the Biden administration of building a “Ministry of Truth” to law enforcement people’s thoughts. Two professors writing an belief column in The Wall Road Journal pointed out that the abbreviation for the new Disinformation Governance Board was only “one letter off from K.G.B.,” the Soviet Union’s protection services.
Alejandro N. Mayorkas, the secretary of the Department of Homeland Protection, has located himself on the defensive. In a tv interview on CNN on Sunday, he insisted that the new board was a small team, that it experienced no operational authority or ability and that it would not spy on Us residents.
“We in the Division of Homeland Stability never monitor American citizens,” he said.
Mr. Mayorkas’s reassurance did little to quell the furor, underscoring how partisan the discussion in excess of disinformation has turn into. Going through a round of thoughts about the board on Monday, the White Dwelling push secretary, Jen Psaki, mentioned it represented a continuation of function that the department’s Cybersecurity and Infrastructure Protection Agency experienced started in 2020, under the former administration.
Its concentrate is to coordinate the department’s reaction to the likely impacts of disinformation threats — such as foreign election impact, like Russia’s in 2016 and all over again in 2020 initiatives by smugglers to stimulate migrants to cross the border and on the internet posts that could incite extremist assaults. Ms. Psaki did not elaborate on how the department would outline what constituted extremist written content on line. She said the board would think about building public its findings on disinformation, whilst “a whole lot of this operate is seriously about work that men and women may well not see each day that’s ongoing by the Office of Homeland Security.”
Several of those people criticizing the board scoured Ms. Jankowicz’s previous statements, on the net and off, accusing her of staying hostile to conservative viewpoints. They suggested — with no basis — that she would stifle lawfully secured speech using a partisan calculus.
Two position Republicans on the Home committees on intelligence and homeland stability — Michael R. Turner of Ohio and John Katko of New York — cited recent comments she manufactured about the laptops of Hunter Biden, the president’s son, and about Elon Musk’s bid to invest in Twitter as proof of bias.
Ms. Jankowicz, 33, has prompt in her reserve and in community statements that condescending and misogynistic content on the internet can prelude violence and other unlawful functions offline — the kinds of threat the board was produced to keep track of. Her ebook cites investigate into virulent reactions that outstanding women have confronted, such as Vice President Kamala Harris right after her nomination in 2020.
Ms. Jankowicz has named for social media businesses and law enforcement businesses to take stiffer motion versus on-line abuse. This sort of views have prompted warnings that the government should not law enforcement information on the internet it has also determined Mr. Musk, who has said he wishes to buy Twitter to free its customers from onerous limitations that in his perspective violate liberty of speech.
“I shudder to consider about, if no cost speech absolutists were being using about additional platforms, what that would be like for the marginalized communities all over the world, which are now shouldering so a great deal of this abuse, disproportionate quantities of this abuse” Ms. Jankowicz advised NPR in an interview past 7 days about her new e-book, referring to all those who experience attacks on the net, primarily gals and folks of color.
A tweet she despatched, utilizing a portion of that estimate, was cited by Mr. Turner and Mr. Katko in their letter to Mr. Mayorkas. The note requested “all documents and communications” about the creation of the board and Ms. Jankowicz’s appointment as its govt director.
The board quietly began perform two months in the past, staffed element time by officers from other parts of the huge section. The Homeland Security Division made the final decision to sort the board last year after it done a research in the summer that suggested establishing a team to evaluate concerns of privacy and civil libertyfor on-line content material, according to John Cohen, the former acting head of the department’s intelligence branch.
“And making absolutely sure that when the department’s components are executing that analysis, they’re operating in a way consistent with their authorities,” Mr. Cohen, who remaining the administration last thirty day period, explained in an job interview.
Mr. Cohen pushed back on promises that the team would be policing language on the net.
“It’s not a big place with feeds from Fb and Twitter popping up,” Mr. Cohen mentioned. “It appears to be at coverage challenges, it appears to be at finest techniques, it appears at tutorial investigate relating to how disinformation influences the menace surroundings.”
Soon after researching plan concerns, the board is then meant to post advice to the homeland security secretary for how distinct agencies really should conduct examination of online material whilst preserving the civil liberties of Us citizens, and how commonly the conclusions of that assessment can be shared.
In accordance to a statement launched on Monday, the section reported the board would keep track of “disinformation unfold by overseas states these as Russia, China and Iran, or other adversaries these as transnational prison companies and human smuggling corporations.” The assertion also cited disinformation that can unfold in the course of organic disasters, like fake info about the protection of ingesting water for the duration of Hurricane Sandy in 2012.
It is not the initial time the Section of Homeland Security has moved to detect disinformation as a risk going through the homeland. The office joined the F.B.I. in releasing terrorism bulletins warning that falsehoods about the 2020 election and the Capitol riots on Jan. 6, 2021, could embolden domestic extremists.
Mr. Mayorkas has defended Ms. Jankowicz, contacting her “a renowned expert” who was “eminently qualified” to advise the department on safety threats that germinate in the fecund environment on the net. At the same time, he acknowledged mishandling the announcement of the board — made in a very simple press assertion past 7 days.
“I assume we almost certainly could have carried out a greater position of communicating what it does and does not do,” he instructed CNN.
Ms. Jankowicz has been a familiar commentator on disinformation for a long time. She has worked for the Nationwide Democratic Institute, an affiliate of the National Endowment for Democracy that encourages democratic governance abroad, and served as a fellow at the Woodrow Wilson Intercontinental Center for Scholars in Washington.
As a Fulbright fellow, she labored as an adviser to the Ukrainian federal government in 2017. Her 2020 guide, “How to Reduce the Data War: Russia, Phony Information and the Future of Conflict,” concentrated on Russia’s weaponization of information and facts. It warned that governments had been unwell organized and ill geared up to counteract disinformation.
A quotation posted on her biography on the Wilson Center’s internet site underscores the challenges for those who would combat disinformation.
“Disinformation is not a partisan trouble it is a democratic just one, and it will acquire cooperation — cross-bash, cross-sector, cross-governing administration, and cross-border — to defeat,” it says.
Security headers are easily overlooked in website audits.
While some may say that website security is not an SEO-related concern, it does become SEO-related when a site becomes hacked and search traffic dwindles to zero.
Security headers should be a top concern of everyone who publishes anything on the Internet.
The good news is that they are relatively simple to configure and will help keep your website and its visitors safe.
in this column, you’ll learn what security headers are and how they work as well as the top 5 security headers, how to implement them, which WordPress plugins you can use for setting security headers, and more.
Let’s get started!
What Are Security Headers?
Security headers are directives browsers must follow that are passed along through the HTTP header response.
An HTTP header is a response by a web server to a browser that is trying to access a web page.
The header response communicates things such as when the web page does not exist (400 response header).
Or that it’s okay to download a font from Google but not to trust any other data outside of the website’s domain.
In that example, the part that tells the browser that it’s okay to download Google fonts but not trust any files originating elsewhere other than the website itself is a security directive.
A security directive like that will block a browser from downloading malicious files from another website.
Security headers introduce restrictions and instructions that prevent unintended security events.
Why Use Security Headers?
Automated bot software are constantly probing and testing websites for security weaknesses.
These vulnerabilities can be introduced by the content management system, by the JavaScript library used to add functionality, and for security weaknesses introduced by a plugin or a theme.
Websites that use security headers are said to be hardened against security threats.
While a website can get along without using security headers by keeping its components up to date and using security plugins, doing so needlessly exposes the website and the site visitors to security risks.
For example, security plugins can’t stop ad injections that rob a site owner of ad revenue.
Perhaps the best reason to use security headers is because they are relatively easy to implement and ensure that a website keeps running normally.
Top 5 Security Headers
1. Content-Security-Policy (CSP)
A content security policy (CSP) helps to protect a website and the site visitors from Cross Site Scripting (XSS) attacks and from data injection attacks.
Cross-Site Scripting (XSS)
Cross-Site Scripting (XSS) exploits happen when hackers take advantage of a security hole to upload malicious scripts to a website which are then downloaded to a victim’s browser.
XSS attacks take advantage of flaws in a content management system that allows unexpected inputs to be injected because of insufficient user input file sanitization.
For example, ordinarily, an email form should be coded to expect a restricted input.
A poorly coded form may allow some other input which can then lead to an injection of malicious files.
An XSS attack can be used to steal passwords or as part of a multi-step hacking event.
Injection Attacks
The Open Web Application Security Project (OWASP) describes injection attacks as a serious security risk:
“Injection is an attacker’s attempt to send data to an application in a way that will change the meaning of commands being sent to an interpreter.
For example, the most common example is SQL injection, where an attacker sends “101 OR 1=1” instead of just “101”. When included in a SQL query, this data changes the meaning to return ALL records instead of just one.
…Frequently these interpreters run with a lot of access, so a successful attack can easily result in significant data breaches, or even loss of control of a browser, application, or server. Taken together, injection attacks are a huge percentage of the serious application security risk.”
The content security policy by itself does not 100{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} protect a site from attacks but it does help to diminish the possibility of a cross site scripting attack.
A CSP header instructs the browser to only download resources from a set group of domains and only from those domains.
Any attacker that is downloading malicious scripts from another server outside of that trusted group will be blocked.
Creating a content security policy can be as strict or as lenient as a publisher requires.
Warning: However, setting one up can be a little tricky because you have to list all of the scripts and resources that are being downloaded from outside of your domain in order to whitelist them.
2. Strict-Transport-Security Header (HSTS)
The Strict-Transport-Security Header is also called the HTTP Strict Transport Security header (HSTS).
Many websites only have a 301 redirect from HTTP to HTTPS.
But that’s not enough to keep the website secure because the website is still vulnerable to a man-in-the-middle attack.
HSTS prevents an attacker from downgrading the HTTPS connection to an HTTP connection which then allows the attacker to take advantage of insecure redirects.
For example, if a person types in example.com to access a site, without actually typing in the https part (or they simply type http out of habit), then the opportunity exists for a man-in-the-middle attack.
That kind of attack can compromise the site visitors’ connection to the website and any sensitive information exchanged between the visitor and the website becomes visible to the attacker.
For example, an attacker can intercept cookies that contain sensitive information like login credentials.
The United States government lists three scenarios where HTTPS can be downgraded to HTTP and subsequently allow an attacker to compromise security.
These are the three ways HTTPS can be downgraded:
When a user types “gsa.gov” into the URL bar, browsers default to using http://.
A user may click on an old link that mistakenly uses an http:// URL.
A user’s network may be hostile and actively rewrite https:// links to http://.
The HSTS header prevents this from happening by forcing the browser to absolutely not accept an HTTP connection.
The HTTP Strict Transport Security (HSTS) header tells the browser that the entire website should only be accessed by a secure HTTPS protocol.
Side Note: How To Preload HSTS Into Chrome
On a related note, Google Chrome has an HSTS Preload program where publishers can submit their sites to be listed by Chrome as only accessible via the HTTPS protocol.
Many Chrome-based web browsers will subsequently preload these websites with HTTPS and only via HTTPS, hard coding that standard right into the browser.
Qualifying sites must already be serving the HSTS security header.
These are the four requirements needed to qualify for Chrome HSTS preloading:
“Serve a valid certificate.
Redirect from HTTP to HTTPS on the same host, if you are listening on port 80.
Serve all subdomains over HTTPS. In particular, you must support HTTPS for the www subdomain if a DNS record for that subdomain exists.
Serve an HSTS header on the base domain for HTTPS requests:- The max-age must be at least 31536000 seconds (1 year).- The includeSubDomains directive must be specified.- The preload directive must be specified.- If you are serving an additional redirect from your HTTPS site, that redirect must still have the HSTS header (rather than the page it redirects to).
This security header stops certain kinds of exploits that can happen, for example, through malicious user-generated content.
Browsers can “sniff” if a content is an image (.jpg), a movie (.mp4), or text, HTML, JavaScript, and other kinds of content that can be downloaded from a website.
The “sniffing” allows a browser to download the web page elements and correctly render them, in particular in situations when the metadata the browser needs to render the element is missing.
Sniffing allows the browser to figure out what the element is (an image, text, etc.) and then render that element.
Hackers however will try to trick browsers into thinking that a harmful JavaScript file is actually an image, allowing the browser to download the file and then subsequently executing that file, causing any number of negative outcomes for that site visitor, especially with what’s known as a Drive-by Download Attack.
The X-Content-Type-Options header can stop that and other related attacks by disabling the ability of browsers from “sniffing” for the content type.
4. X-Frame-Options
The X-Frame-Options security header helps stop click-jacking attacks.
“Framesniffing is an attack technique that takes advantage of browser functionality to steal data from a website.
Web applications that allow their content to be hosted in a cross-domain IFRAME may be vulnerable to this attack.
The X-Frame-Options header can be used to control whether a page can be placed in an IFRAME.
Because the Framesniffing technique relies on being able to place the victim site in an IFRAME, a web application can protect itself by sending an appropriate X-Frame-Options header.”
The Open Web Application Security Project (OWASP) provides a helpful explanation of click-jacking attacks:
“…imagine an attacker who builds a web site that has a button on it that says “click here for a free iPod”.
However, on top of that web page, the attacker has loaded an iframe with your mail account, and lined up exactly the “delete all messages” button directly on top of the “free iPod” button.
The victim tries to click on the “free iPod” button but instead actually clicked on the invisible “delete all messages” button.
In essence, the attacker has “hijacked” the user’s click, hence the name “Clickjacking”.”
The X-Frame-Options header is important for protecting your site visitors as well as your site’s reputation.
The OWASP web page on click-jacking goes on to describe how Adobe Flash fell victim to a click-jacking attack that allowed hackers to take control of microphones and cameras, thus cementing Flash’s negative reputation as a security nightmare.
Becoming known across social media and the greater Internet as a security hazard is bad for business.
The X-Frame-Options header is a useful security measure to implement.
5. Referrer-Policy
The purpose of a Referrer-Policy header is to allow a website publisher to control what information is sent when a site visitor clicks a link to visit another website.
When a site visitor clicks a link and lands on another site, the visitor’s browser provides information about what web page sent that visit.
When you look at your server logs the referrer information is sent that tells what sites sent visitors.
However, there are some situations where the URL of the site referring a visitor to another visitor could contain sensitive information which could be leaked to a third party.
How the Referrer-Policy works is by limiting how much information is sent after a site visitor clicks a link.
A website publisher can choose to send no information as to the referrer, they can choose to send just the domain name or they can send the entire URL string.
There are eight directives that can be sent using the Referrer-Policy header:
Referrer-Policy: no-referrer.
Referrer-Policy: no-referrer-when-downgrade.
Referrer-Policy: origin.
Referrer-Policy: origin-when-cross-origin.
Referrer-Policy: same-origin.
Referrer-Policy: strict-origin.
Referrer-Policy: strict-origin-when-cross-origin.
Referrer-Policy: unsafe-url.
A common referrer policy setting is Header “no-referrer-when-downgrade” which means that referrer information will be sent to trustworthy URLs that are on HTTPS but that no referrer information will be sent to untrusted HTTP websites.
It is important to note that the referrer policy setting will not affect affiliate links.
The referrer information is coded within the landing page URL, thus the referrer information and earnings are recorded by the merchant receiving the affiliate referral.
How To Implement Security Headers
There are multiple ways to set security headers, and one popular way is with an .htaccess file.
A benefit of using the .htaccess file is that it saves a publisher from downloading another plugin.
Poorly coded plugins can become a security risk, so minimizing the number of installed plugins can be useful.
Important: Every security header implementation is going to be different according to the specifics of each website, especially the Content-Security-Policy (CSP).
WordPress Plugins For Setting Security Headers
There are some popular plugins that are already installed on millions of websites that come with the option for setting security headers.
If you already have these plugins installed, then the option for using a plugin rather than fussing with an .htaccess file is there for those who would prefer the convenience.
Really Simple SSL Pro
Over five million websites already have Really Simple SSL installed.
Upgrading to the reasonably priced pro version provides the option for setting up to eight security headers the easy way.
Redirection
The 100{4224f0a76978c4d6828175c7edfc499fc862aa95a2f708cd5006c57745b2aaca} free WordPress Redirection plugin has been around for over ten years and is installed on over 2 million websites.
This plugin allows you to choose from many different preset security headers in addition to the top five listed in this article.
Preset means that you can choose from the standard directives.
According to the Redirection WordPress download page:
“ADD HTTP HEADERS HTTP headers can be added to redirects or your entire site that help reduce the impact of redirects or help increase security. You can also add your own custom headers.”
Additionally, the Redirection plugin allows you to custom craft your own security headers if there’s something there you don’t find.
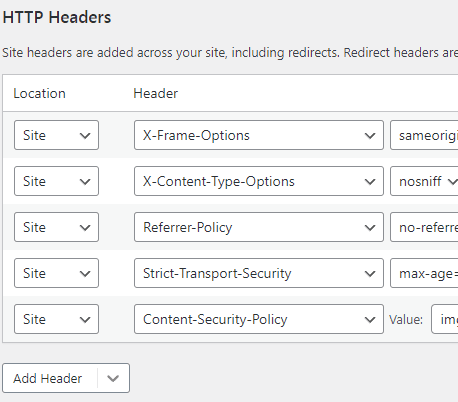
Screenshot of Security Headers UI, February 2022
The Redirection plugin makes it easy to successfully install the top five security headers:
“Attaching headers To attach headers to Cloudflare Pages responses, create a _headers plain text file in the output folder of your project.
It is usually the folder that contains the deploy-ready HTML files and assets generated by the build, such as favicons.
The _headers file should not always be in the root directory of the repository. Changes to headers will be updated to your website at build time, so make sure you commit and push the file to trigger a new build each time you update headers.
Header rules are defined in multi-line blocks.
The first line of a block is the URL or URL pattern where the rule’s headers should be applied. On the next line, an indented list of header names and header values must be written…”
Web auditing software Screaming Frog also has the option for checking headers which is available in the Security Tab.
Make Security Headers A Part Of Your SEO Audits
Security headers are something that many publishers or SEO experts might not consider.
But security headers are important and should be top of mind in every site audit, whether that audit is conducted in-house or by third-party SEO site auditing.
Website security is an SEO-related issue because failure to mitigate negative security issues can reverse every ranking-related success.
A negative reputation can hurt rankings and sales.
Loss of search visibility causes devastating losses.
Implementing security headers is relatively easy, it should be among the top boxes to check when publishing any website.
More resources:
Featured Image: Monkey Business Images/Shutterstock
The federal government has unveiled a new set of voluntary ideas aimed at supplying guidance to organisations in how they safeguard vital systems from cyber attacks.
Labelled the Critical Know-how Provide Chain Concepts, Minister of Dwelling Affairs Karen Andrews claimed the voluntary principles were being developed to give organisations and individuals the self esteem to allocate a lot more methods in the direction of important emerging systems this kind of as synthetic intelligence, quantum computing, blockchain, and algorithmic automation.
“These principles occur at a important time — both for Australia and for our essential industries. We deal with unprecedented threats from a selection of malicious cyber actors, growing geostrategic uncertainty, and are ever more reliant on technologies that can be hacked, held to ransom, or if not disrupted,” Andrews stated.
The ideas had been formulated in partnership with field, non-govt organisations, state and territory governments, and the community.
There are 10 new rules in complete, with the 4 of them staying: Understand what requires to be secured, why it wants to be guarded, and how it can be protected realize the unique protection risks posed by an organisation’s provide chain establish security concerns into all organisational procedures, which includes into contracting processes that are proportionate to the amount of chance and elevate awareness of and endorse protection inside source chains
In relation to these 4 concepts exclusively, House Affairs hopes they will allow for fewer-resourced organisations to carry out appropriate actions for protectecting essential technological innovation.
“When safety is developed in by-design it also suggests customers do not will need to have qualified awareness and that they are not unfairly transferred hazard that they are not best positioned to control,” Home Affairs stated.
The remaining rules are: Know who crucial suppliers are and create an comprehending of their security measures established and connect minimum transparency requirements reliable with present criteria and global benchmarks for suppliers encourage suppliers to realize and be transparent in the depth of their source chains, and be able to give this information and facts to clients request and think about the accessible assistance and advice on affect of overseas governments on suppliers look at if suppliers operate ethically, with integrity, and constantly with intercontinental law and human rights and develop strategic partnering associations with vital suppliers.
Dwelling Affairs warned that thought of these concepts are vital as the absence of protection measures can have movement-on impacts to the broader community and Australia’s countrywide desire.
As element of the concepts getting declared, Andrews said the federal government by itself would be employing the concepts for its personal conclusion-creating methods.
“Alongside essential legislation at present ahead of the Senate to assist and aid significant industries confront cyberattacks, broad adoption of these new ideas will safeguard Australia’s protection, and prosperity for years to occur,” Andrews included.
The launch of the ideas follows the federal federal government recently distributing a revised Safety Laws Modification (Significant Infrastructure) Invoice 2020 into Parliament. The revised Bill is a stripped-down version of the original edition, only that contains the elements that would introduce govt assistance mechanisms and required notification specifications.
In the meantime, components of the Invoice that have been cut out will be considered in a long term Invoice down the highway.
The Invoice was revised in reaction to recommendations created by the Parliamentary Joint Committee on Intelligence and Stability, which claimed this two-phase tactic would enable the swift passage of legislation to counter looming threats versus Australia’s vital infrastructure, whilst supplying firms and govt further time to co-layout a regulatory framework that offer prolonged-phrase security for the country’s vital infrastructure.
The federal governing administration is also acquiring a new established of standalone felony offences for people today who use ransomware as part of its Ransomware Action Program.